Check Point escapes ChatGPT's Lockdown Mode: a preview popup left the sandbox with the whole chat history
Check Point escaped ChatGPT's Lockdown Mode sandbox via an HTML-preview popup, exposing full chat history; OpenAI patched it server-side on September 18.
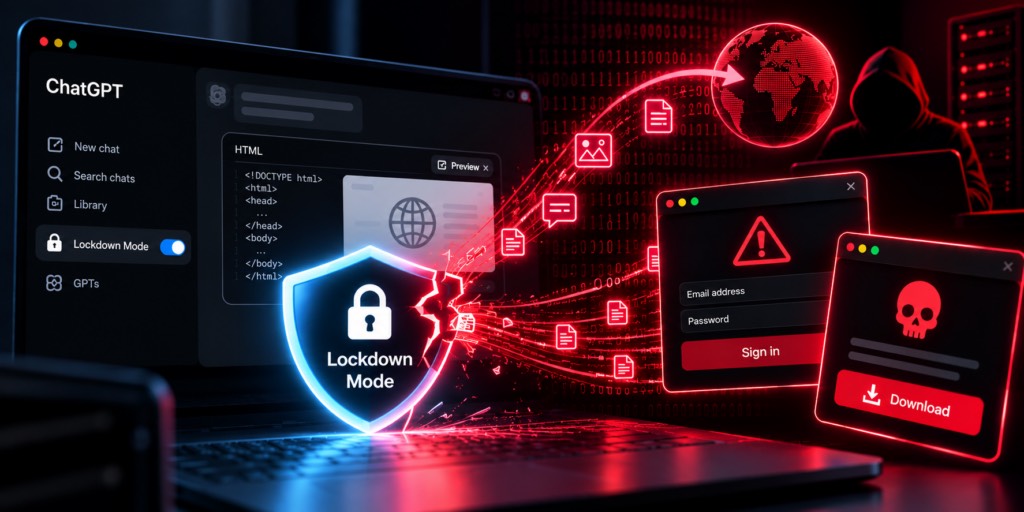
Check Point Research (CPR), the security research arm of Check Point, published the full escape chain for a bypass of ChatGPT’s Lockdown Mode on November 5. The HTML page preview that renders inside ChatGPT code blocks runs in a sandboxed iframe, but its sandbox attribute kept two permissive tokens, allow-popups and allow-popups-to-escape-sandbox. By nesting one more iframe inside the preview page and calling its native window.open, researcher Alexey Bukhteyev opened a popup that lives entirely outside the sandbox. In CPR’s demonstration that popup silently ships the entire chat history and uploaded files to an attacker-controlled server. OpenAI removed the two tokens in a server-side fix deployed on September 18, 2026; CPR retested and confirmed the technique no longer works, and users needed no client update.
Key points
- The escape lives in the host application, not the model: the outer iframe of ChatGPT’s HTML preview kept
allow-popupsandallow-popups-to-escape-sandbox, and a nested iframe’s untouched nativewindow.openbypasses ChatGPT’s popup-approval hook. - Beyond data theft, CPR demonstrated phishing popups that keep the ChatGPT app icon, a forced sign-out followed by a fake re-login page to harvest credentials, and malware served through a fake “ChatGPT update” dialog.
- The fix went out server-side: OpenAI told CPR on September 18, 2026 that it had stripped the two popup tokens from the preview sandbox. There is no CVE number and, as of November 6, no separate OpenAI announcement.
Background
Lockdown Mode is OpenAI’s optional security setting, announced on February 13, 2026 for “a small set of highly security-conscious users” — the announcement names executives and security teams as examples. Turning it on limits live web access to cached content, drops internet images from responses, and disables Deep Research, Agent Mode, Canvas networking, live connectors and file downloads; features OpenAI cannot guarantee deterministically are switched off rather than hardened. It first covered enterprise-style workspaces (Enterprise, Edu, Healthcare, Teachers) and reached personal accounts under Settings > Security, together with self-serve Business plans, on June 4, 2026. The complication is that in the same February, ChatGPT also shipped HTML page previews inside code blocks — a routine capability improvement, rendered in sandboxed nested iframes. The two features arrived together, and the preview sandbox’s default permissions turned out to be the widest gap in Lockdown Mode’s perimeter.
| Date | Event |
|---|---|
| 2026-02-13 | OpenAI announces Lockdown Mode for Enterprise, Edu, Healthcare and Teachers workspaces |
| 2026-02 | HTML page previews ship in ChatGPT code blocks, inside sandboxed nested iframes |
| 2026-06-04 | Lockdown Mode reaches personal accounts and self-serve Business plans |
| 2026-09-18 | OpenAI tells CPR the fix is deployed: the two popup tokens removed from the sandbox |
| 2026-11-05 | CPR publishes the technical write-up and analysis |
| 2026-11-06 | TechRadar covers the disclosure: “AI security controls depend on the wider environment” |
The Lockdown Mode bypass
Each step of the bypass lands on an implementation detail of the preview feature. The isolation itself worked as designed: the HTML preview runs in nested iframes, direct reads of chatgpt.com cookies and localStorage are blocked, the main app interface is out of reach, and external requests need approval. ChatGPT additionally hooks window.open — popups require user approval, and calls with an empty URL or about:blank silently return null, which closes the usual automation paths. The gap Bukhteyev found is nesting: inside the sandboxed page, create one more iframe and call its contentWindow.open. That resolves to the real, un-hooked window.open, so the override never runs. The outer sandbox attribute’s allow-popups-to-escape-sandbox token finishes the job — the popup opens outside the sandbox, and every outbound restriction Lockdown Mode enforces stops applying to it. As CPR summarized the mechanism, “the underlying sandbox permissions still allowed popups and permitted them to escape the sandbox.” Nowhere in the chain does the model get talked into anything; the whole escape is a permissions configuration on the host application.
What was at risk
The impact runs from silent data theft to credential capture. The most direct scenario is exfiltration: the escaped popup can send the entire chat history and the user’s uploaded files to an attacker-controlled server with no visible cue. Phishing comes next — the popup keeps the ChatGPT app icon while the attacker controls its title and content, which is enough to impersonate a trusted system dialog. CPR also showed the main window being reloaded and the user being forced into a sign-out, then steered onto a fake re-login page that collects credentials. Malware delivery rides the same trust: a fake “Download ChatGPT update” popup. Per CPR, an attack “could potentially originate from a malicious prompt, malicious GPT or shared chat, depending on the scenario” — the shared-chat browser variant does not require the victim to be logged in. Desktop is worse: in the Electron-based ChatGPT Classic app, window.open needs no user gesture at all, and “simply having a conversation is enough to trigger the attack.” File downloads still require one click, and CPR notes the technique is not limited to the desktop environment.
What others say
Check Point framed the finding at two levels. The analysis post is bylined by Eli Smadja, Head of Research, and lands on one sentence: “AI security controls are only as strong as the wider application environment around them.” The technical write-up ends more concretely — guardrails and built-in security features help mitigate threats but offer “no absolute guarantee of protection,” and “every new capability expands the attack surface, including features built purely for convenience.” Its advice for enterprises runs four items: gain visibility into AI usage, control the sensitive data shared with AI services, treat runtimes and connectors as part of the AI attack surface, and limit exposure to third-party platforms. TechRadar (Sead Fadilpašić, November 6) folds the story into the same wider frame and singles out the zero-click desktop scenario. OpenAI’s side is the thinnest layer: as of November 6, 2026 we could not find a separate OpenAI announcement, so the fix’s timing and mechanics rest entirely on CPR’s account and its retest.
Our take
For developers building GPTs, agents or shared experiences on ChatGPT, three things are worth carrying away. First, the security boundary is drawn by the host application, not the model: your product runs inside someone else’s iframe sandbox, and what failed was two tokens granted too generously by default. When you audit your own product, a checklist item for leftover sandbox permissions beats hindsight. Second, server-side patching changes the responsibility structure: the platform changed a security property without any user-visible signal, fixing on September 18 and surfacing publicly on November 5 — for nearly seven weeks users had nothing to check against. If you stake sensitive workflows on a single platform, expect invisible changes of this kind. Third, read this month as a series: the AI event invite phishing that bypassed MFA attacked trust in AI brands, Claude Code putting user emails into User-Agent headers attacked the boundary between assistant and outside world, this escape attacked the platform’s own isolation layer, and OpenAI’s autonomous pipeline producing 948 kernel exploits shows the supply of new attacks is itself accelerating. The honest catch: no CVE, no OpenAI announcement, a single-source timeline, and no disclosed dates for discovery and reporting; the zero-click claim has only been demonstrated in the Electron desktop app, while the browser scenario still needs one user action. The Lockdown Mode bypass itself is closed — what it tested, how concretely a platform cashes its security promises, will be tested again on the next feature.